ISO/IEC 27001:2013
Professional credential details
ISO/IEC 27001:2013
Category: Governance & Compliance
Type: Training
Issuing Organization: ABSHAR
Year: 2014
Summary
Applying ISO/IEC 27001 principles and requirements to support the effective management and governance of information security.
Description
Knowledge of ISO/IEC 27001 and Information Security Management System (ISMS) principles for establishing, managing, assessing, and continually improving information security practices. Skilled in understanding information security policies, risk assessment and treatment, security controls, compliance requirements, internal assessment, and continual improvement. Able to align information security management with organizational objectives, IT governance, risk management, and business requirements.
Certificate
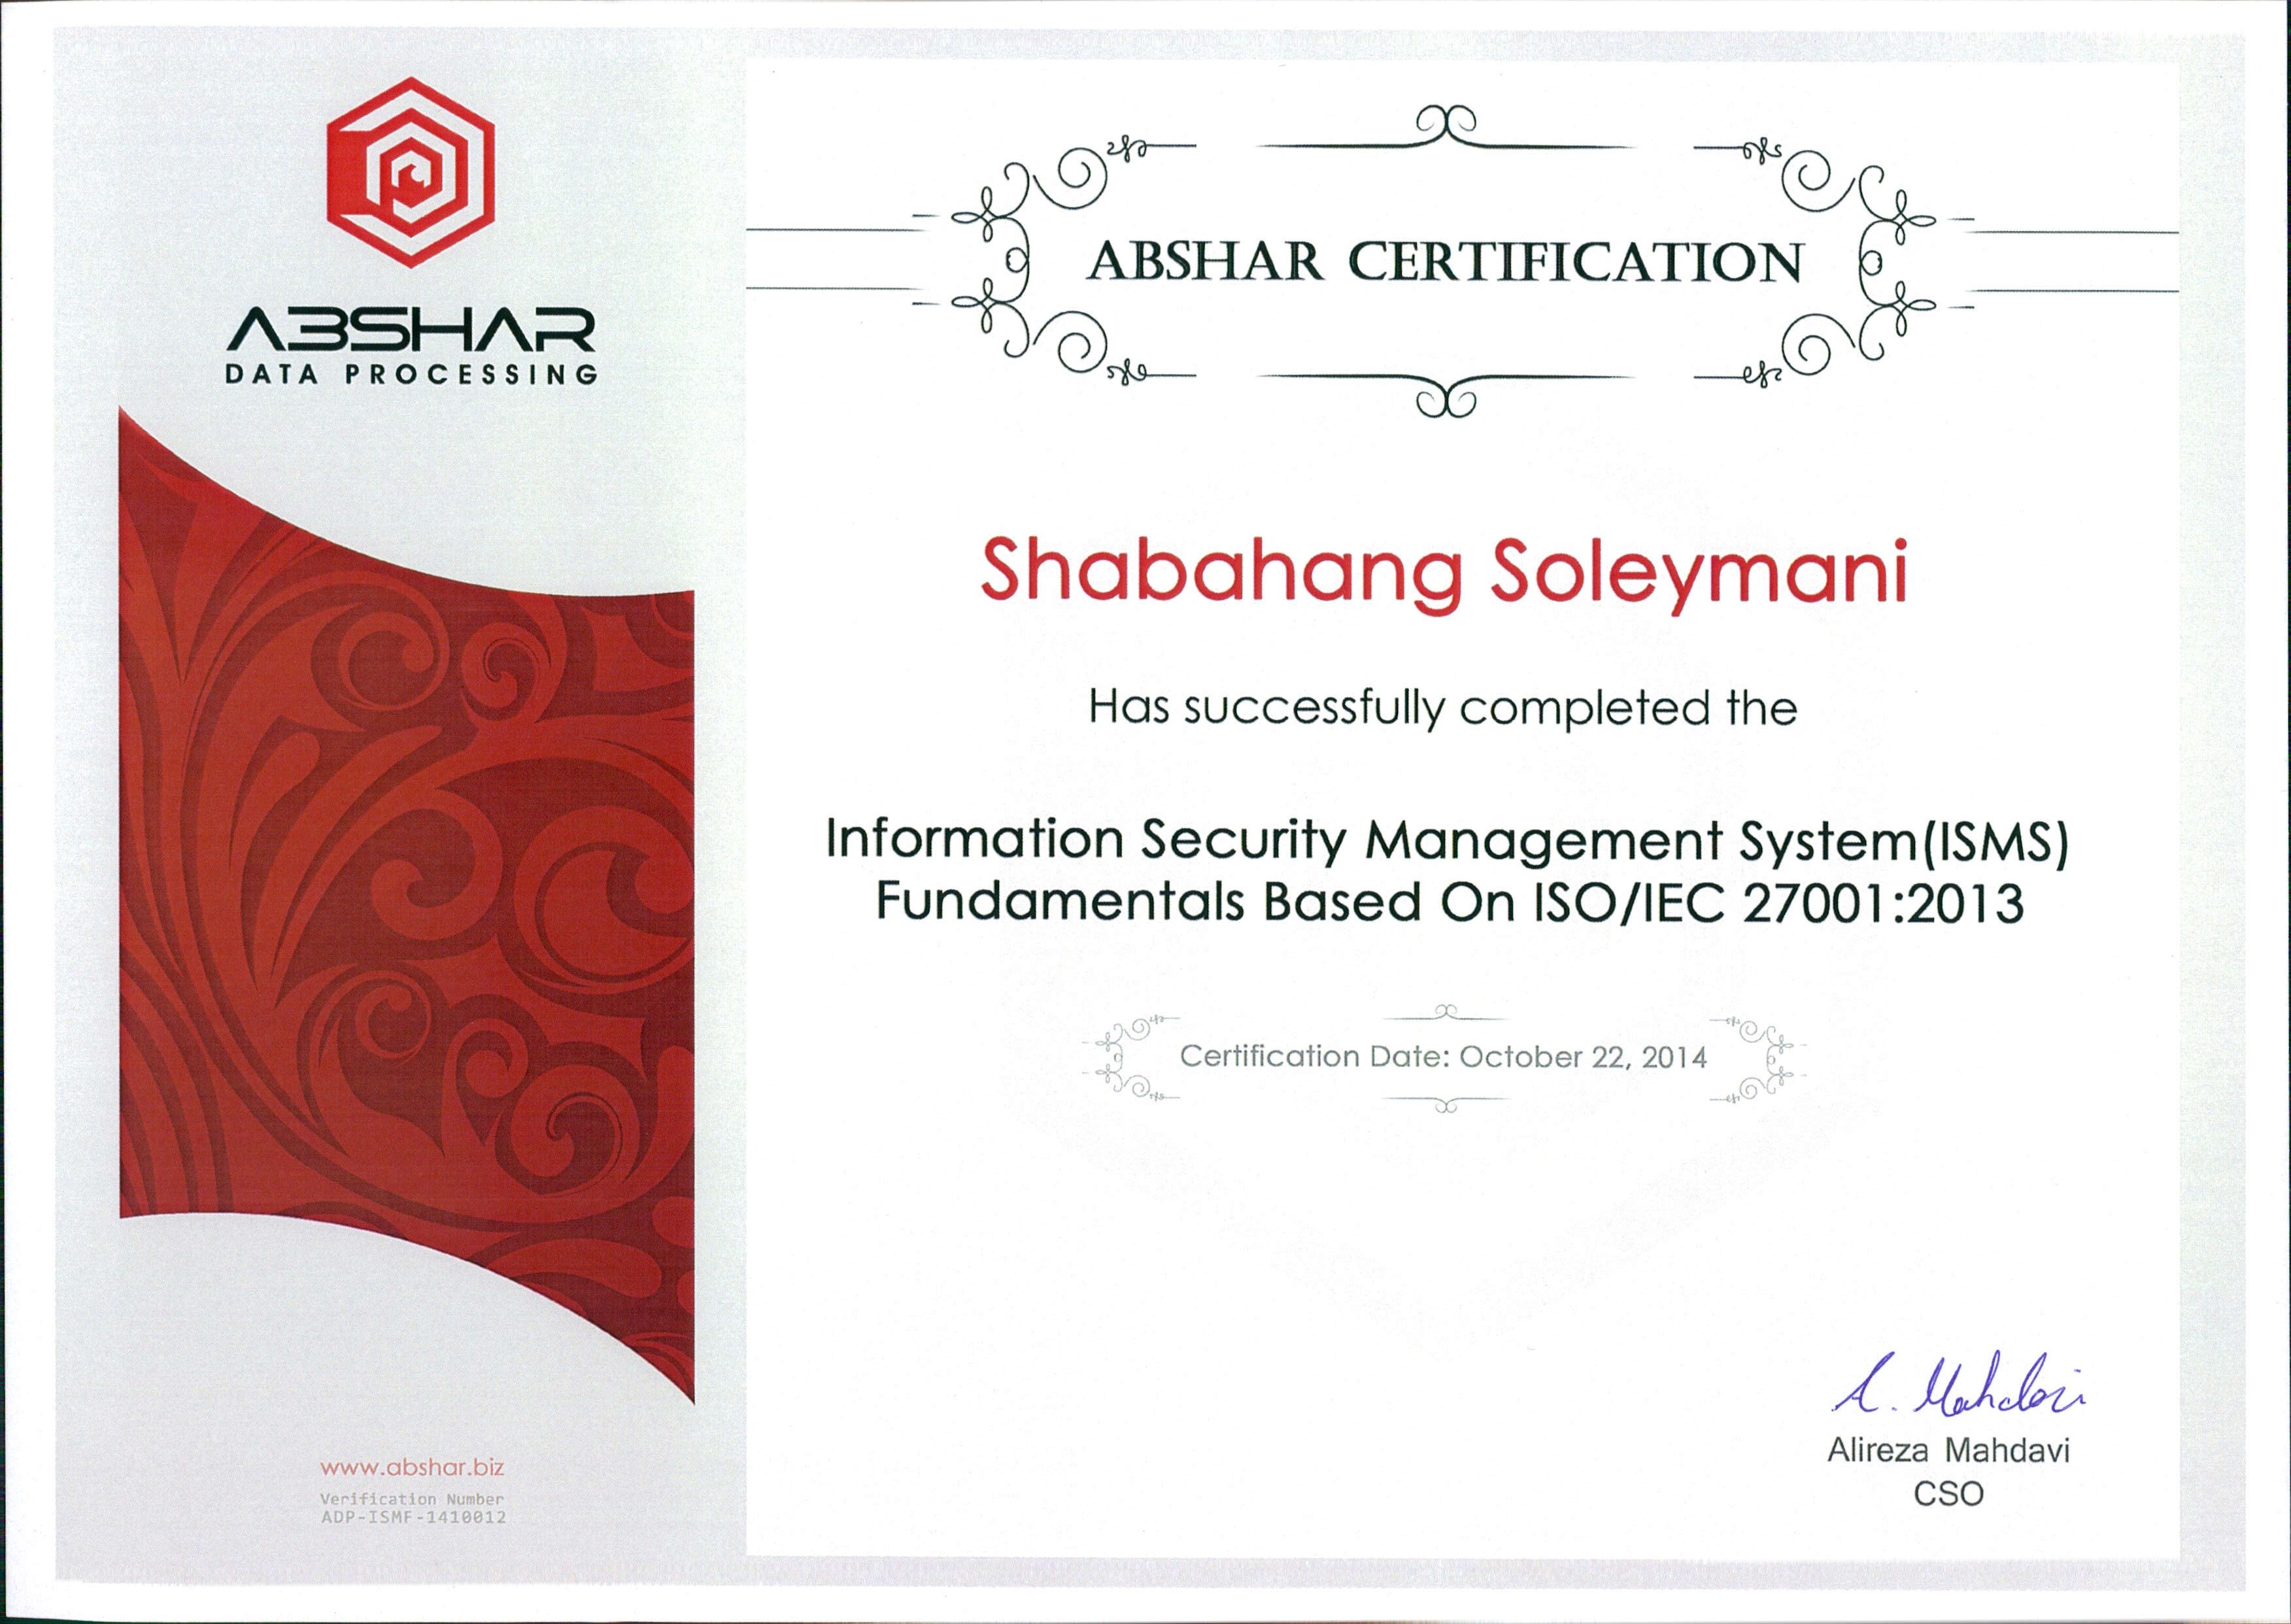
Click the certificate image to view it in full size.